
Building a Crypto Trading Bot for Multiple Exchanges: Engineering Considerations
How multi-exchange crypto trading software is scoped, including venue differences, connector design, state handling, safeguards, and operations.
 Sun Cluster Inc.
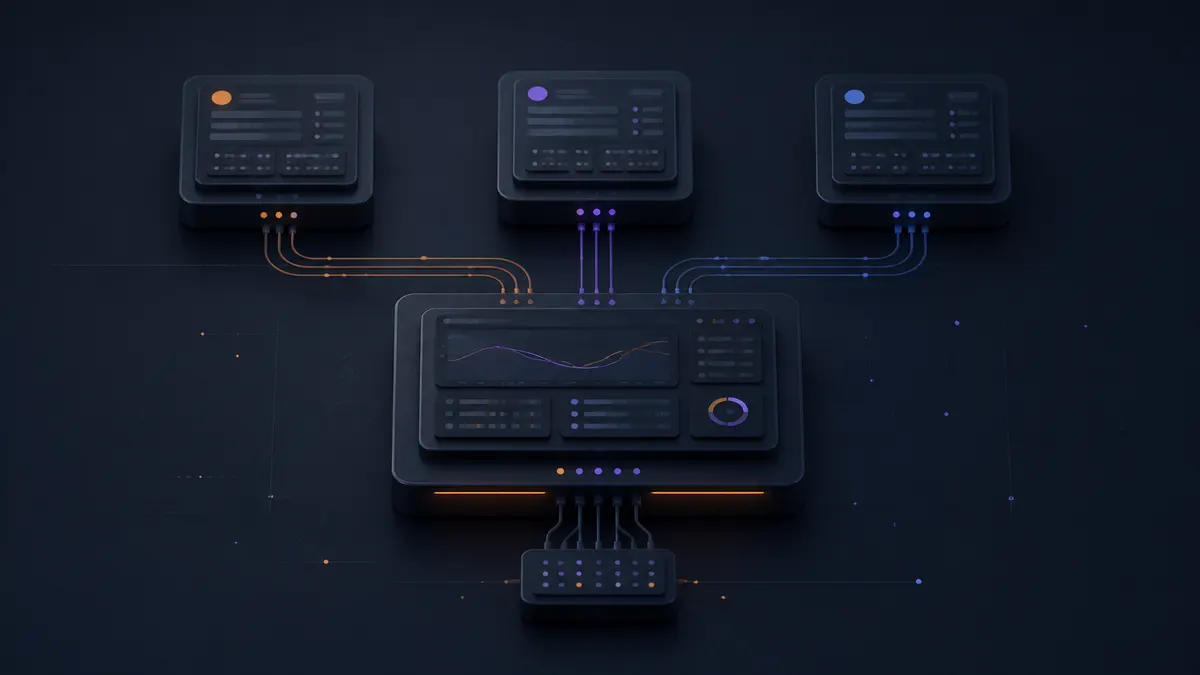
A multi-exchange trading system needs a clear boundary between shared strategy logic and venue-specific behaviour. That separation makes it easier to operate, test, and change without pretending every exchange works the same way.
Start with the operational scope
Decide whether the system only submits client-defined instructions or also needs account views, reconciliation, alerts, and operator controls. A narrow connector and a production operating system have very different scopes.
Keep venue differences at the edge
Exchange connectors should translate each venue's symbols, precision rules, order types, authentication, and response formats into a stable internal model. The strategy layer should not need to guess which venue-specific rule applies.
- Pair naming and quantity precision
- Order and cancellation capabilities
- Account type and permission boundaries
- Rate limits and connection limits
Treat market data as a separate concern
Price feeds, snapshots, and streaming updates can arrive at different speeds and with different completeness guarantees. Record which feed is authoritative for each workflow, how stale data is detected, and what happens when a feed drops.
Design for order state, not only order submission
An accepted request may be open, partially filled, rejected, cancelled, or changed by the venue. Persist the client request, venue response, and later updates so an operator can reconcile what the software believes with the venue record.
Build safeguards into the connector
Controls can include allow-listed instruments, quantity limits, duplicate-request protection, pause states, and visible alerts. The right controls depend on the client-defined workflow; they are not a substitute for a trading decision or a guarantee of outcome.
Plan the operating work
API credentials expire, venue behaviour changes, and network failures happen. Agree on logging, alert ownership, deployment access, and the path for connector maintenance before a system is put into use.
Validate each venue connector independently
A shared strategy layer does not make venue behaviour interchangeable. Verify each connector against its own permissions, symbols, precision, order states, cancellation behaviour, limits, and recovery path. Record the outcome so a change to one connector does not silently affect another.
The operating team also needs to see connector health, stale data, and whether a requested action was accepted by the venue. That visibility is more meaningful than a broad claim of multi-exchange support.
- Controlled venue test path
- Normalized and original venue responses
- Connector health and stale-data signals
- Reconciliation for each venue
Common questions
Can one trading rule run on every exchange?
Only after the differences in instruments, precision, available order types, account permissions, and market data have been assessed. A shared rule still needs venue-aware execution handling.
Why is reconciliation needed?
It gives operators a way to compare local state with venue-reported orders, fills, balances, or positions after interruptions or ambiguous responses.
Can one exchange connector simply be copied for another?
No. The architecture can share patterns, but each venue’s API, permissions, precision, and state behaviour needs its own validation.
Does multi-exchange support mean the same strategy works across venues?
No. This is an engineering discussion about software boundaries and integrations. Strategy decisions and financial outcomes remain the client’s responsibility.
Discuss your software project
Have a defined workflow, integration, or delivery question? Tell us about the technical constraints and the outcome your team needs to support.
Contact Sun Cluster